FYDO API Security Changes

How the move from Legacy API Keys to HMAC authentication affects your FYDO API integrators, and what to do before enforcement.

FYDO is enhancing security around API usage. The authentication model is changing from Legacy API Keys to a HMAC (Hash-Based Message Authentication Code) model.

There will be a 2-month grace period where the Legacy API Key model will be supported, while hospital API Integrators work towards transitioning to the HMAC method of authentication.

IMPORTANT — From 8 October 2026, only HMAC-authenticated API calls will be accepted. Any calls using Legacy API Keys will fail from this date.

A guide on HMAC integration will be advised shortly in a follow up email to all Facilities identified as having API Users.

What’s Changing

Security screen changes

  • Existing API Keys are now hidden.
  • A key can now be rotated manually, which also gives the old key a 72-hour grace period, so the old key will work for 72 hours, giving integrators time to change to the new key at a time that suits them.

New API Integrators screen

  • All existing API Users from the Security screen automatically have an Integrator ID set up.
  • Under each Integrator, there is now the ability to add a contact email and phone number.
  • All API endpoints are listed, with permissions that can be set to “Allowed” or “Not Allowed” for each user.
  • An IP address allow list is available to restrict API Integrators to specific IP addresses.
  • An HMAC Secret Key can be generated to support the new method of making API calls, which will be replacing the Legacy API Key in 2 months’ time.

API Log screen

  • A new Audit Log screen is available, logging changes made to the API Integrator screen.

Security Screen

Under this screen, you will have a 1-time opportunity to edit any API Usernames that are generic, such as “FYDO User”, so these users can be properly identified by the name only.
A warning screen will prompt you to update any usernames upon the first save.
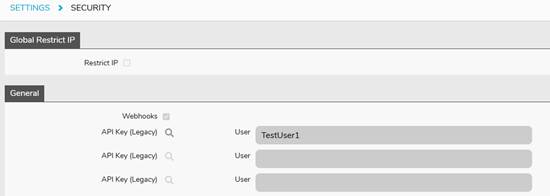
Settings > Security

If an API Key is lost or forgotten, it will need to be rotated:

  1. Click on the Edit button.
  2. Click on the Rotate API Key (Legacy) button to generate a new API Key.
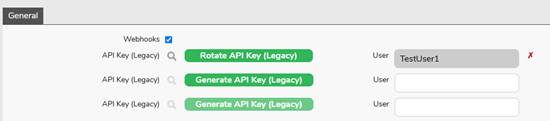
Rotating a Legacy API Key

  • Copy the API Key shown and click Confirm to save.
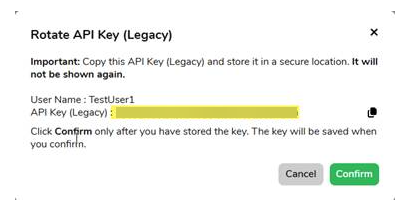
The new key is shown once — copy it before confirming

Integrators Screen

All existing API Users that were set up in the Security screen will have an Integrator ID created within the Integrators screen. This ID is used along with the HMAC Secret Key generated on the same screen, which will replace the Legacy API Key for authentication in 2 months.

To access the Integrators screen:

  1. Go to Settings > Integrators, under the API menu.
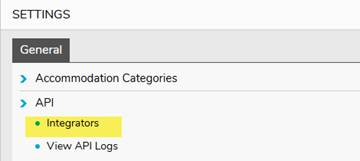
Settings > API > Integrators

2. Open an Integrator’s settings by clicking on the Integrator.
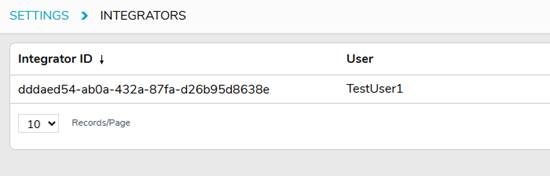
The Integrators list

3. Within the Integrator screen, you can:

  • Add the contact details (email and phone) of the API Integrator, used for future contact.
  • Generate an HMAC Secret Key, used for authenticating API calls along with the Integrator ID.
  • Set a restriction on IP addresses that are allowed to make API calls to your FYDO database.
  • Set Endpoint Permissions — to either allow or deny access to particular data within FYDO.
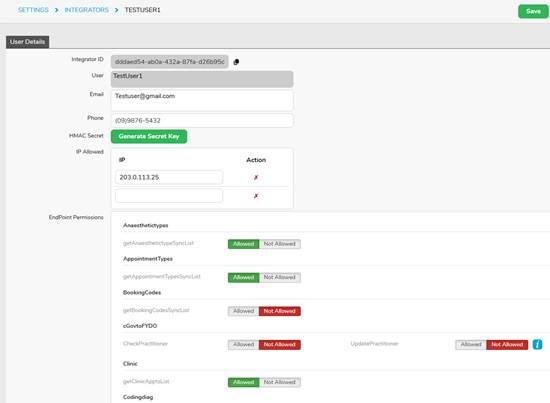
Integrator detail — contact details, HMAC Secret, IP allow list and Endpoint Permissions

Note — Existing API users will have permissions all set to “Allowed”, but it is encouraged to set permissions to “Not Allowed” for endpoints the API Integrator doesn’t need.
New API Users created will have all Endpoint Permissions set to “Not Allowed” by default, so will need to be enabled for all required endpoints.

The details of each endpoint are described in the FYDO Wiki here: FYDO API Details – FYDO Wiki

Creating an HMAC Secret Key

The HMAC Secret Key is the new method of authenticating an API Integrator with your FYDO database. This is required along with the Integrator ID.

To create an HMAC Secret Key:

  1. While editing the Integrator screen, click on the Generate Secret Key button.
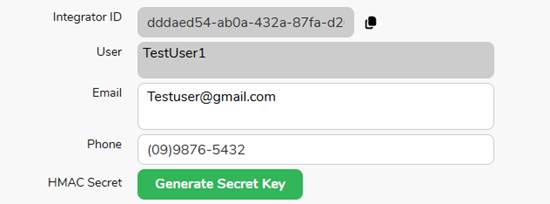
Generate Secret Key

  • Click Yes to confirm.
  • Click the copy button to copy the key and store it securely, then confirm to save the HMAC Key.
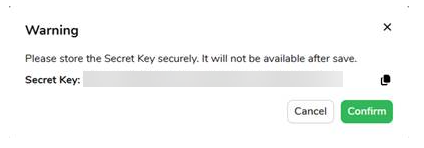
The Secret Key is shown once — copy it before confirming

Regenerating a Lost or Forgotten HMAC Secret Key

  1. Edit the Integrator screen.
  2. Click on the Regenerate Secret Key button, and click Yes to confirm.
  3. Copy the new key and store it securely.

Disabling/Re-enabling an API Integrator

  1. Under the Integrators list, click on the Action function
  2. Click on the “Disable Access” button
  3. Click on Yes to confirm
  4. Once confirmed the Status will show “Inactive” for that Integrator and they will not be able to make any further API calls.
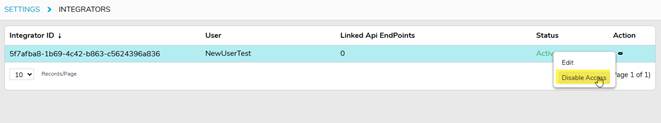
Note- Under the same action function, you can re-enable an Integrator which will give them access also.
Single Sign On (SSO) with FYDO

At FYDO, we are committed to continuously enhancing the security and convenience of our platform for our valued customers. And because of that, we use Single Sign On (SSO) to FYDO! This feature will allow you to access FYDO using your existing credentials from Microsoft or Google, simplifying your login process while maintaining the highest level of security.

SSO is a secure authentication process that enables you to log in to multiple applications with a single set of credentials. By integrating SSO, we aim to provide you with a seamless and efficient log in experience.

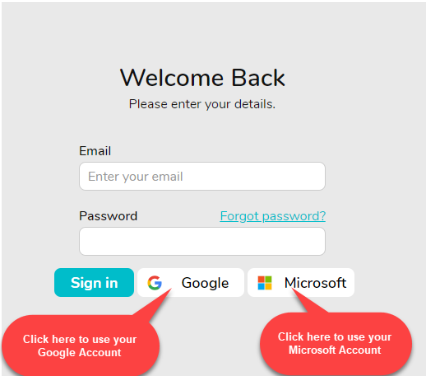
When you log in, you will notice two buttons for Microsoft and Google account access, as pictured below.

If you are already logged into your browser with either a Google or Microsoft account, you can click on the applicable button to log in. This will take you directly to the FYDO dashboard or the Two-Step Verification Process via SMS, email, or an Authentication App as usual. 

Note– The account you use must already be set up in FYDO to proceed. 

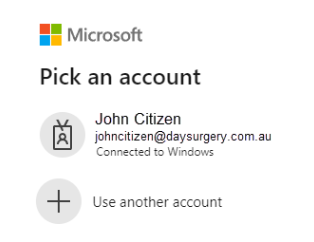
If you are not already logged into your browser with an account, you will be prompted to ‘Pick an account’ or ‘Use another account’ as shown below. You will need to enter your password to proceed. 

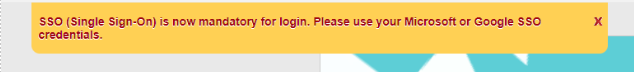
You may still use your email and password to log in unless your FYDO account subscriber has forced SSO to be used. In that case, you may receive a message at the top of the screen, as shown: 

If you receive the message above, please try using the Microsoft or Google buttons. If you still have problems logging in, contact your FYDO account subscriber (the person in charge of FYDO at your facility) before reaching out to Altura Health Support. 

If you have forgotten your Microsoft or Google password, please contact your IT department. This issue is separate from FYDO and cannot be addressed by Altura Health Support.

How to enforce SSO in FYDO

SSO authentication can be enforced for all or selected users. Once SSO is enforced, an email invitation will be sent to the applicable user/s, advising them to activate their account via SSO. The user does not need to use the email invitation link; they can go directly to the FYDO website. 

Note: Once a user is required to use SSO by their facility, their existing password will be deleted. 

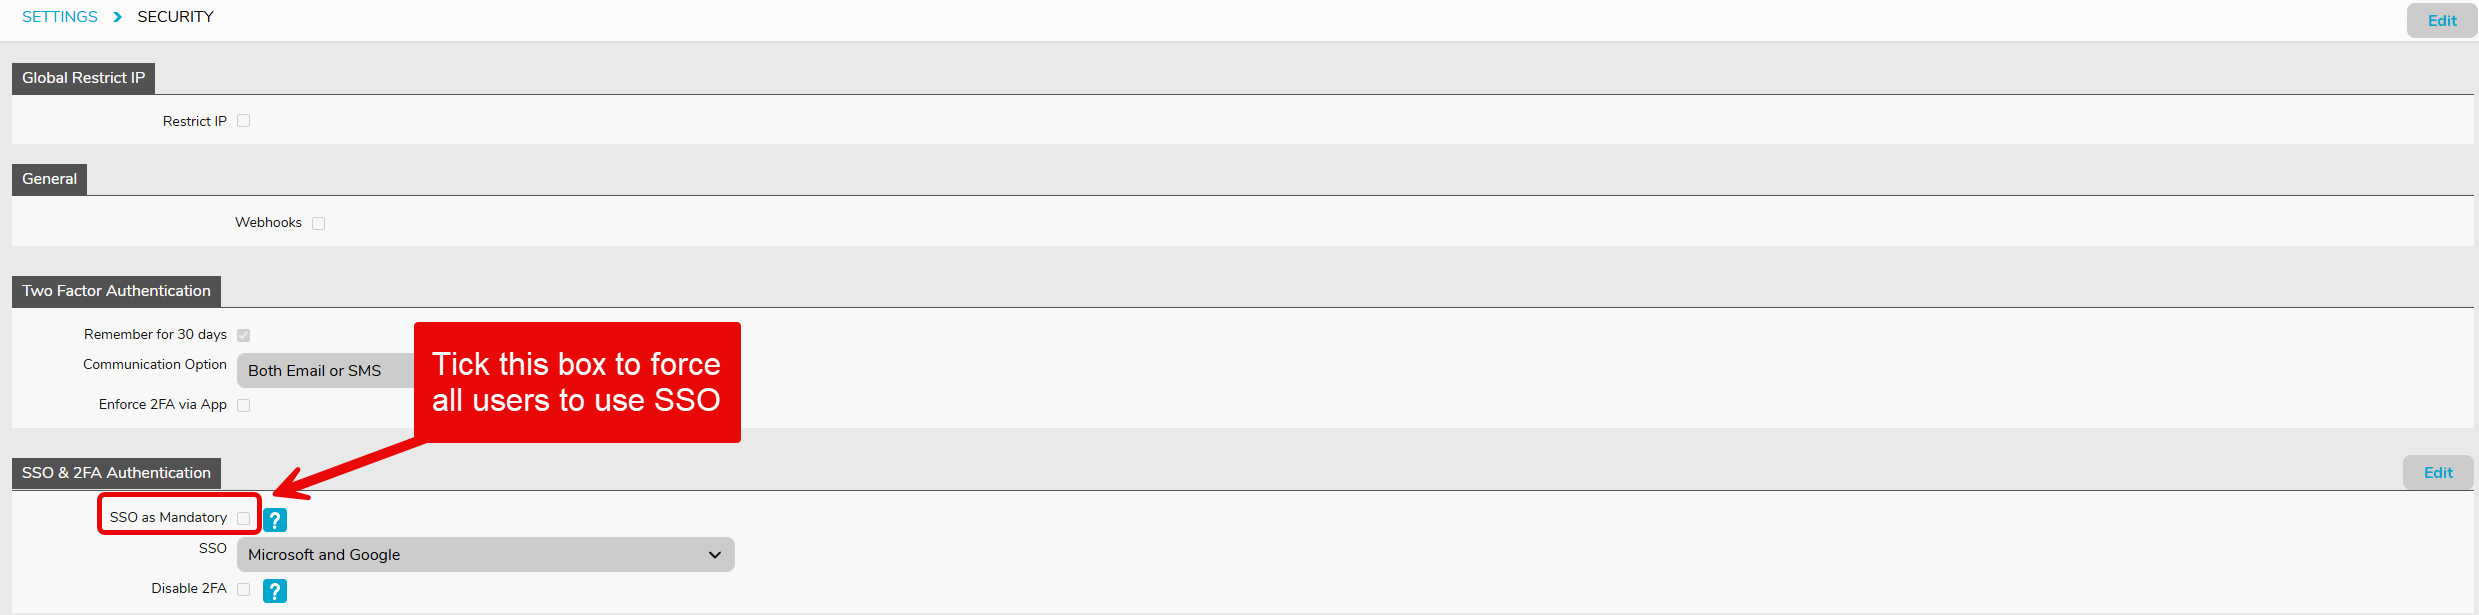
To enforce SSO for all users: 

  1. Go to Settings > Security and click Edit. 

  1. Tick the SSO as Mandatory tick box (as shown below) and click Save. 

If, for any reason, some users are unable to authenticate using SSO, they can be reverted back to the standard email/password authentication method. 

To revert all users to email/password authentication:

  1. Simply untick the SSO as Mandatory box in Settings > Security. 

To revert specific users to email/password authentication: 

  1. Go to Settings > Users
  2. Double-click on required user
  3. Click Edit
  4. Untick SSO Mandatory
  5. Click Save

Reverted users will receive another email invitation to set up their new password. 

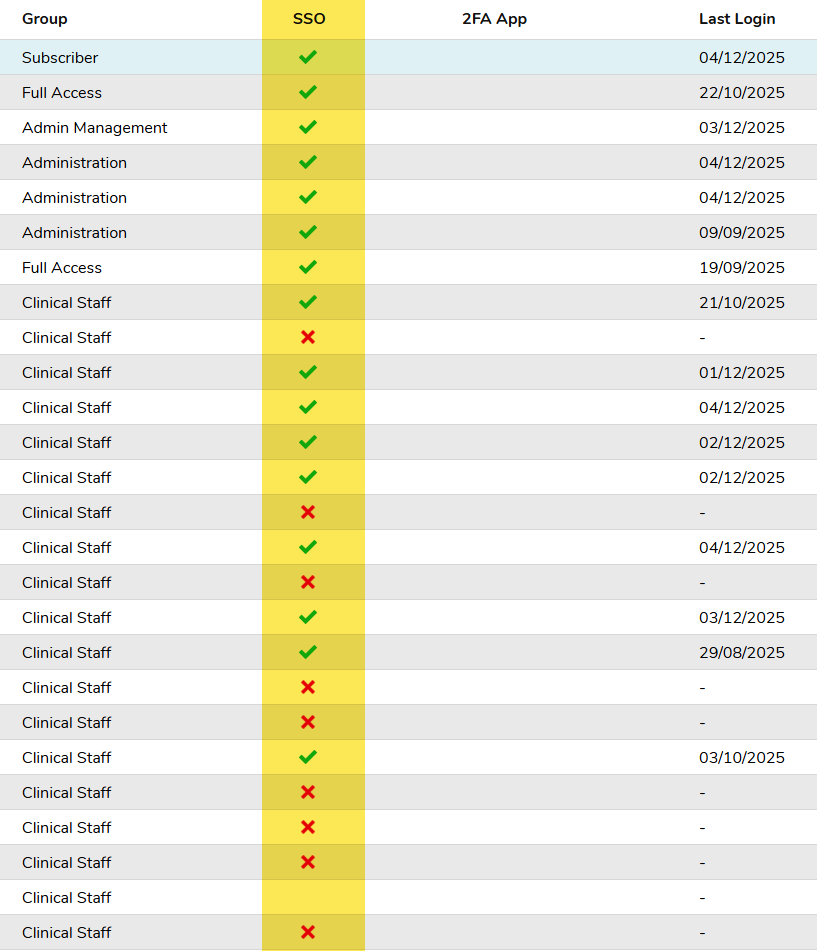
You can see which users have SSO enforced and whether they have successfully authenticated using SSO by going to Settings > Users.  

  • SSO Blank: User not forced to use SSO
  • SSO Red Cross: User forced to use SSO but not activated
  • SSO Green Tick: User has activated SSO


FYDO Security

Rest easy, knowing your FYDO data is protected with layered security controls designed for healthcare environments.

 Secure Infrastructure

  • Hosted on AWS in Australia, leveraging robust cloud security and reliability controls.
  • High availability options are supported for increased redundancy.
  • Backup and restoration strategies are in place to minimise downtime and data loss.

Data Protection

  • Data is encrypted in transit and at rest.
  • Encryption applies to stored data and backups.
  • Data handling is governed by documented policies and access controls.

Identity and access management

  • Supports Single Sign-On (SSO).
  • Multi-Factor Authentication (MFA) is enforced for account access.
  • Role-based access controls (RBAC) support least privilege access, users only receive the access they need for their role.
  • Administrative access is tightly controlled and monitored.

Security Operations, Monitoring and Auditability

  • Continuous monitoring and protective controls are used to detect and respond to suspicious activity.
  • Web application protection controls help defend against common online threats.
  • Centralised logging and alerting support traceability and operational oversight.
  • Audit trails support investigation and accountability for key system events.

Secure Development and Change Control

  • Secure-by-design practices are applied throughout the software lifecycle.
  • Changes are managed through controlled processes to reduce risk and support service stability.
  • Vulnerability management practices are in place to identify and remediate security issues.

Independent Testing and Assurance

  • FYDO undergoes regular independent security testing (e.g. penetration testing and security assessments) by third-party security specialists.
  • Further security documentation and evidence can be provided during procurement or due diligence, subject to confidentiality arrangements.

Incident Management

  • We maintain incident response processes to manage security events, including investigation, containment, and follow-up improvements.


FYDO Two-Step Authentication

FYDO manages highly sensitive information, which is why Two-Step Verification is mandatory for all users.

Each facility can choose whether users must complete the Two-Step Verification process on every log in, or if they will allow users to choose the option to Remember me for 30 days.

Using an Authenticator App (like Google Authenticator) is the most efficient and reliable way to complete your Two-Step Verification. It’s faster and more dependable than receiving codes by SMS or email, especially in areas with poor reception or slow internet.

You may choose SMS & Email authentication if needed. Just note that delivery can be delayed in low-connectivity areas.

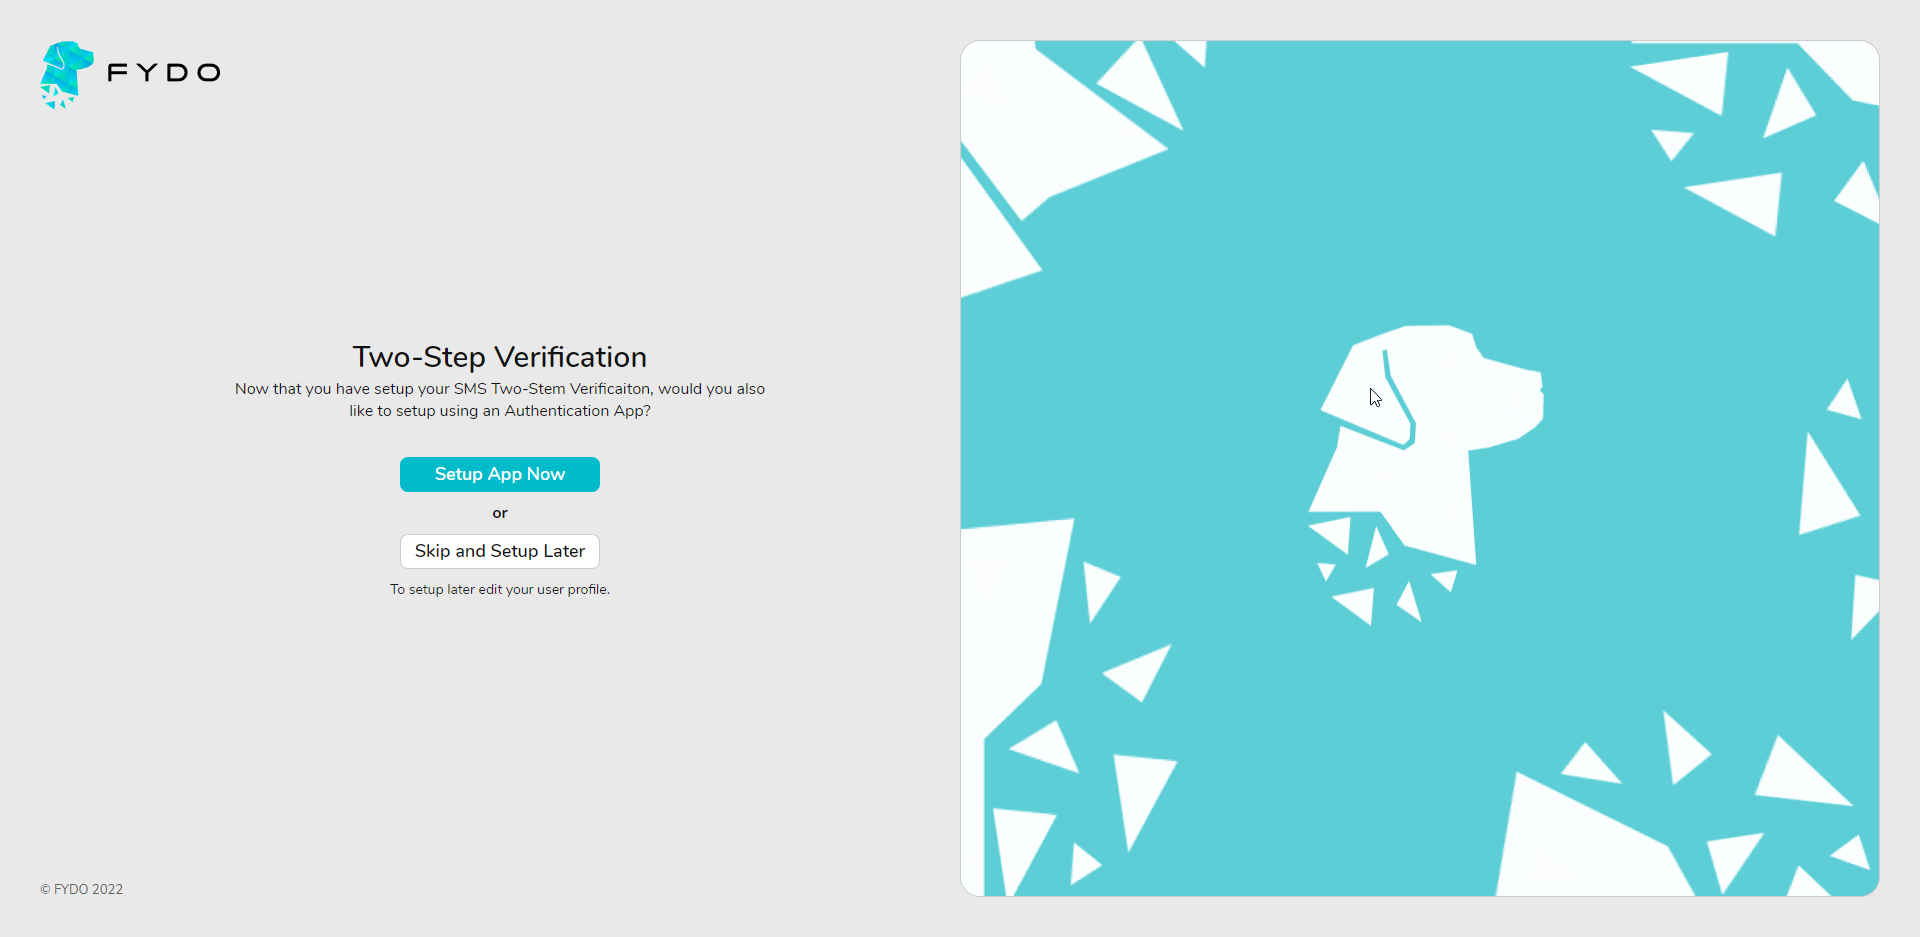
During first log in – You’ll be prompted to Setup App Now.

Download and open the Google Authenticator App on your mobile device. 
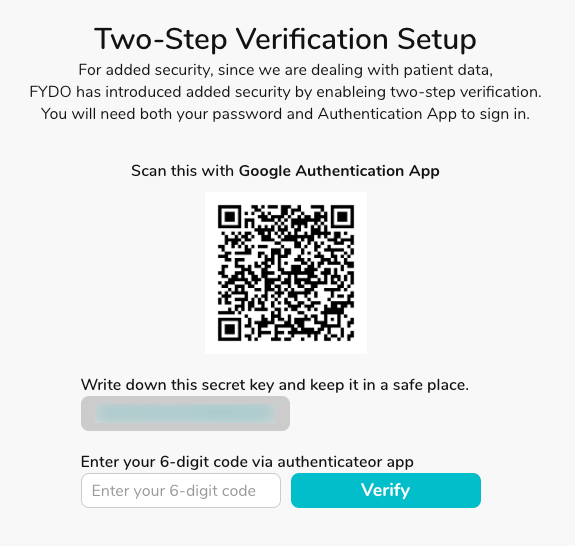
Once the user clicks Setup App Now, on FYDO, they will be shown a QR Code that they can utilise the app to scan.

Open the Google Authenticator App & click Add a Code. Then select Scan a QR Code. 

After following the prompts on the app, the user will be able to obtain their 6-digit code to enter into the field before clicking Verify.
(Writing down the secret key & keeping it in a safe place will allow users to access their account in the case that they misplace their mobile phone)

Want to set up later? Just click Skip and Setup Later. You can continue with SMS or Email verification and set up the app when you’re ready.

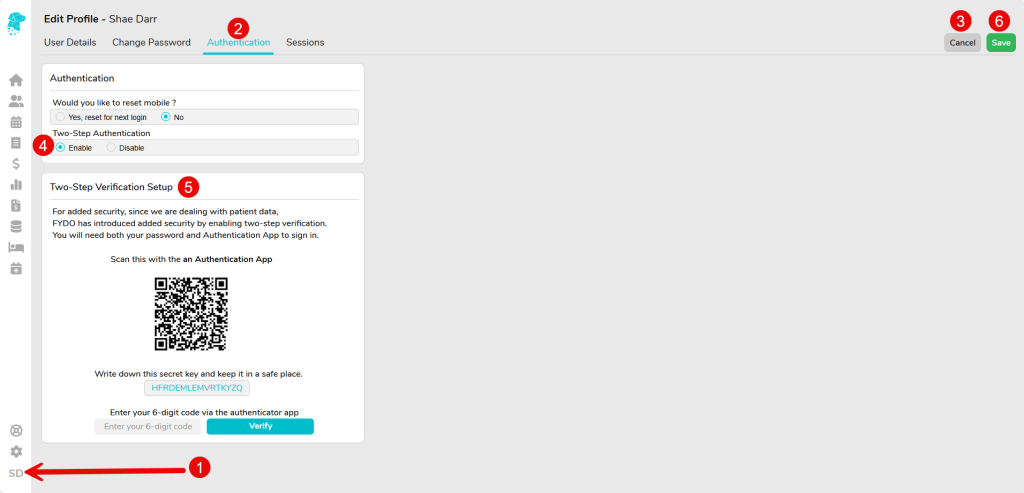
Activating the Authenticator App Later

To enable app-based verification later:

  1. Go to your User Profile and click Edit Profile
  2. Open the Authentication tab
  3. Click Edit 
  4. Tick the Two-Step Authentication > Enable box
  5. Follow the instructions on the page
  6. Click Save


If the facility allows users to utilise the Remember me for 30 days option, then the authentication process will only need to be performed once a month. However, if this function isn’t allowed by the facility, then this authentication process will need to be met each log in.


Altura Health Data Storage & Security Policy

This policy explains, at a high level, how Altura Health safeguards information to prevent loss, unauthorised access, or misuse. It also outlines our approach to backups and restoration.

Data Storage and Residency

  • Customer data is hosted in Australia using AWS.
  • Data is encrypted in transit and at rest using industry-standard encryption.
  • Access to systems and customer data is controlled using least privilege principles and role-based access.

Data Governance and Handling

  • Data access is restricted to authorised personnel and governed by documented processes.
  • Logging and auditability controls support traceability and accountability.
  • Data retention and deletion are managed in line with contractual and regulatory obligations.

Backups and Restoration

  • Backups are performed regularly using cloud-native services.
  • Backups frequency and retention vary depending on the product, environment, and data type (e.g. databases vs documents).
  • Backup storage is protected using access controls and safeguards to reduce the risk of unauthorised access, deletion or modification.
  • Restoration procedures are documented and maintained. Recovery time depends on the nature of the incident and the impacted component.

Monitoring and Assurance

  • Operational monitoring is used to support backup integrity and availability.
  • Periodic backup checks and restore testing are performed to validate recoverability.

Security Assurance

  • Altura Health undertakes regular independent security testing (e.g. penetration testing and security assessments) with third-party specialists.
  • A summary of recent security assessment results may be provided on request, subject to appropriate confidentiality arrangements.

Account Access

  • Altura Health Supports Single Sign-On (SSO) where configured and enforces Multi-Factor Authentication (MFA) for account access.
  • Altura Health supports RBAC, and each facility decides the role structure and is responsible for assigning and maintaining user access for their team.
  • Authentication and access controls may vary depending on customer configuration and agreed requirements.